Back to skill

Security audit

PowPow രജിസ്ട്രേഷൻ — കുമിള രജിസ്റ്റർ ചെയ്യുക, യാത്രാക്കുറിപ്പ് ഭൂപടത്തിൽ പിൻ ചെയ്യുക, ഡിജിറ്റൽ മനുഷ്യരുമായി സംസാരിക്കുക

Security checks for vulnerabilities and agentic risk

Overview

This is a documentation-only PowPow registration and subscription guide with no executable code or credential collection.

Install this if you want Malayalam guidance for creating and activating a PowPow account. Do not share passwords, email verification codes, or payment credentials with the agent; complete registration and payment only on the official PowPow pages.

Vulnerability Patterns
  • Skill Instruction HijackingAlters the agent's session goals or safety constraints when the skill loads
  • Agent Memory PoisoningWrites attacker-controlled rules into memory that affect later sessions
  • Remote Payload Retrieval and ExecutionFetches external code whose behavior can change after review
  • Embedded Malicious CodeShips malicious scripts inside the skill and executes them locally
  • Unauthorized Access and Privilege EscalationObtains permissions beyond the task's legitimate needs
Vulnerability Patterns
  • Prompt InjectionInstruction Override, Hidden Instructions, Exfiltration Commands
  • Trigger AbuseOverly Broad Trigger, Shadow Command Trigger, Keyword Baiting Trigger
  • MCP Tool PoisoningHidden Instructions, Unicode Deception, Parameter Description Injection
  • Data ExfiltrationExternal Transmission, Env Variable Harvesting, File System Enumeration
  • Privilege EscalationExcessive Permissions, Sudo/Root Execution, Credential Access
Findings (6)

Hidden Instructions

High
Category
Prompt Injection
Confidence
60% confidence
Finding

Hidden instructions were detected in comments or invisible text. These could contain malicious directives. Manual review is recommended.

Content

Scanner excerpt · references/screenshots.md (reported line 48)May include surrounding context.

md
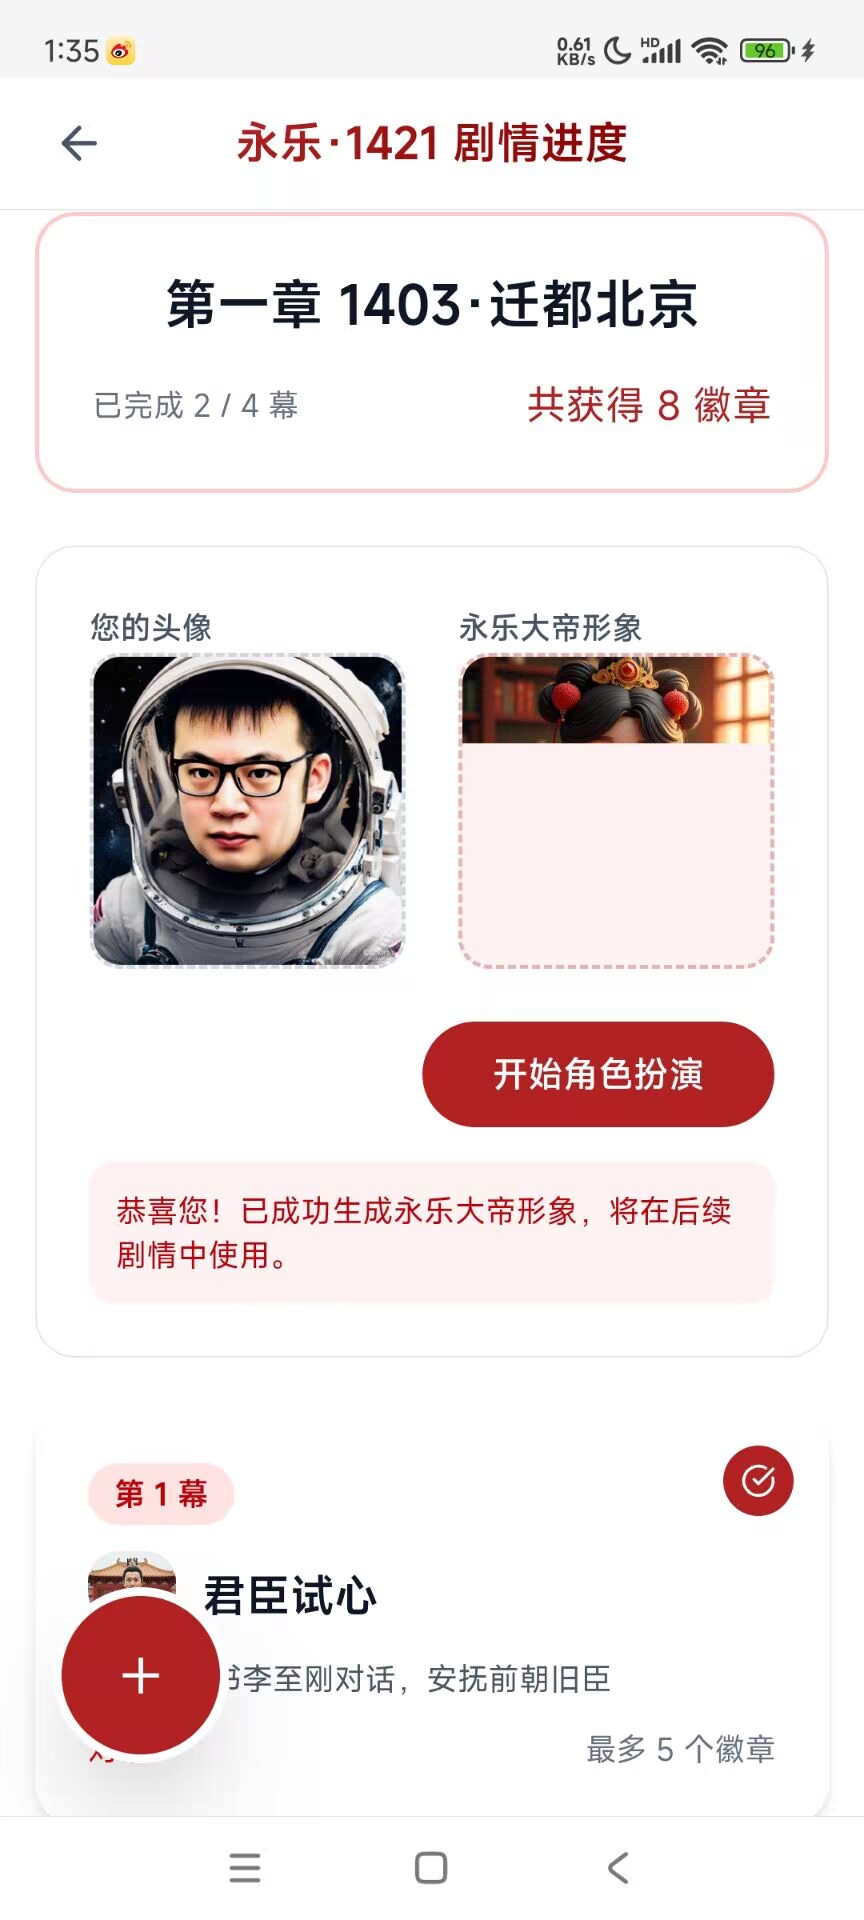
![സ്റ്റോറി പ്രോഗ്രസ് പേജ്](https://raw.githubusercontent.com/durenzidu/durenzidu/main/screenshots/powpow-05.jpg)

പ്ലാറ്റ്ഫോമിലെ സ്റ്റോറി ഗെയിംപ്ലേ (ഉദാഹരണം 「യോങ്ങ്‌ലെ·1421」): അധ്യായ പുരോഗതി, ബാഡ്ജ് നേടൽ, റോൾ പ്ലേ.
**ഉപയോഗിക്കുന്നത്**: ഉപയോക്താവ് "പോസ്റ്റ് ചെയ്യുന്നതിന് പുറമെ മറ്റെന്ത് കളിക്കാം" "ബാഡ്ജ് എങ്ങനെ നേടും" എന്ന് ചോദിക്കുമ്പോൾ.

### powpow-06.jpg — പോസ്റ്റ് വിശദാംശ പേജ് (പൂർത്തിയായ ഉദാഹരണം)

Natural-Language Policy Violations

Medium
Category
Not specified by scanner
Confidence
90% confidence
Finding

The skill description is written entirely in Malayalam, and the README does not indicate that users can choose another language or that Malayalam is required for a justified regional context. This creates a language/locale policy concern because the skill appears to impose a specific language without user opt-in.

Content

No source excerpt is available for this finding.

Natural-Language Policy Violations

Medium
Category
Not specified by scanner
Confidence
93% confidence
Finding

The manifest explicitly sets the language to "ml", and the visible user-facing fields are written in Malayalam. This indicates a fixed language choice, but the file does not document any user opt-in or region-specific justification for restricting the skill to that locale.

Content

No source excerpt is available for this finding.

Natural-Language Policy Violations

Medium
Category
Not specified by scanner
Confidence
89% confidence
Finding

This reference file forces a specific language throughout the skill documentation, while also including user-facing guidance about payments and activation. Under the policy, locale or language constraints should either be optional for the user or explicitly justified; this file provides neither.

Content

No source excerpt is available for this finding.

Intent-Code Divergence

Medium
Category
Not specified by scanner
Confidence
77% confidence
Finding

Lines L17-L19 explicitly state that a command-line/chat skill cannot and should not make payments on the user's behalf or ask for payment credentials. Later, L51-L53 document an existing Alipay payment code path with automatic fallback to simulated payment, which creates tension with the earlier prohibition because it describes a callable payment mechanism rather than a purely redirect-only role.

Content

No source excerpt is available for this finding.

Natural-Language Policy Violations

Medium
Category
Not specified by scanner
Confidence
95% confidence
Finding

The file is primarily written in Malayalam, but it specifies a Chinese-only login error message as the expected user-facing output. Similar forced Chinese strings appear throughout the troubleshooting section, and the document does not indicate any user opt-in, locale selection, or region-specific justification for requiring that language.

Content

No source excerpt is available for this finding.

Static analysis

No suspicious patterns detected.